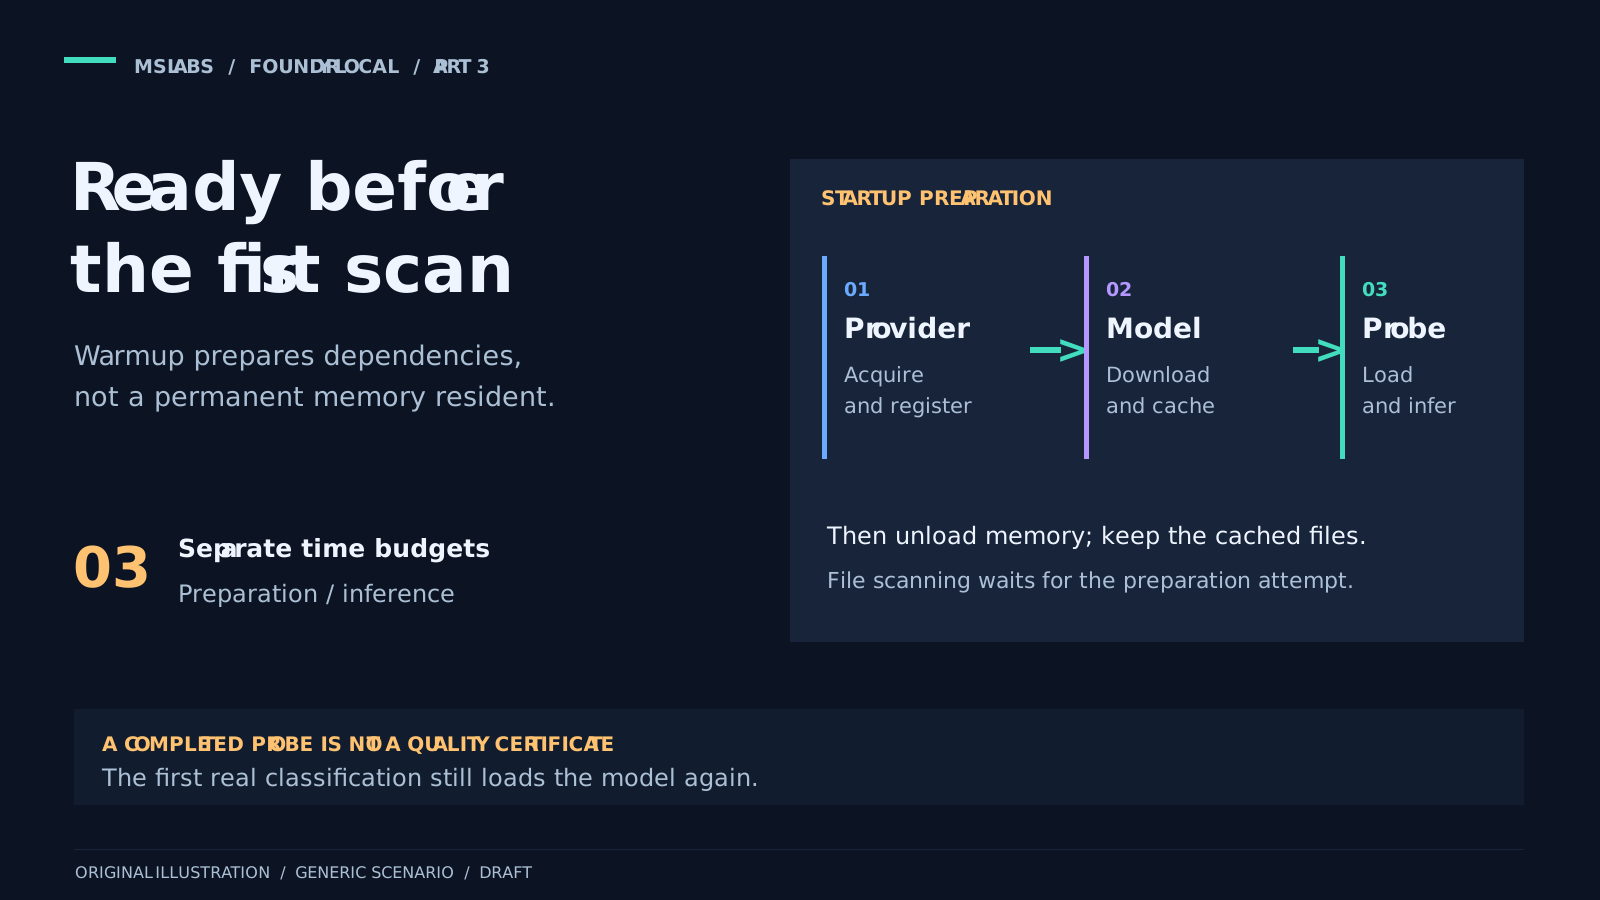
Download and prepare the approved model and execution provider before scanning files. A startup probe helps, but the parser and real workflow need their own checks.
Foundry Local: from local inference to useful file organization · Part 2
Foundry Local · OneDrive · Local AI · File organization · .NET
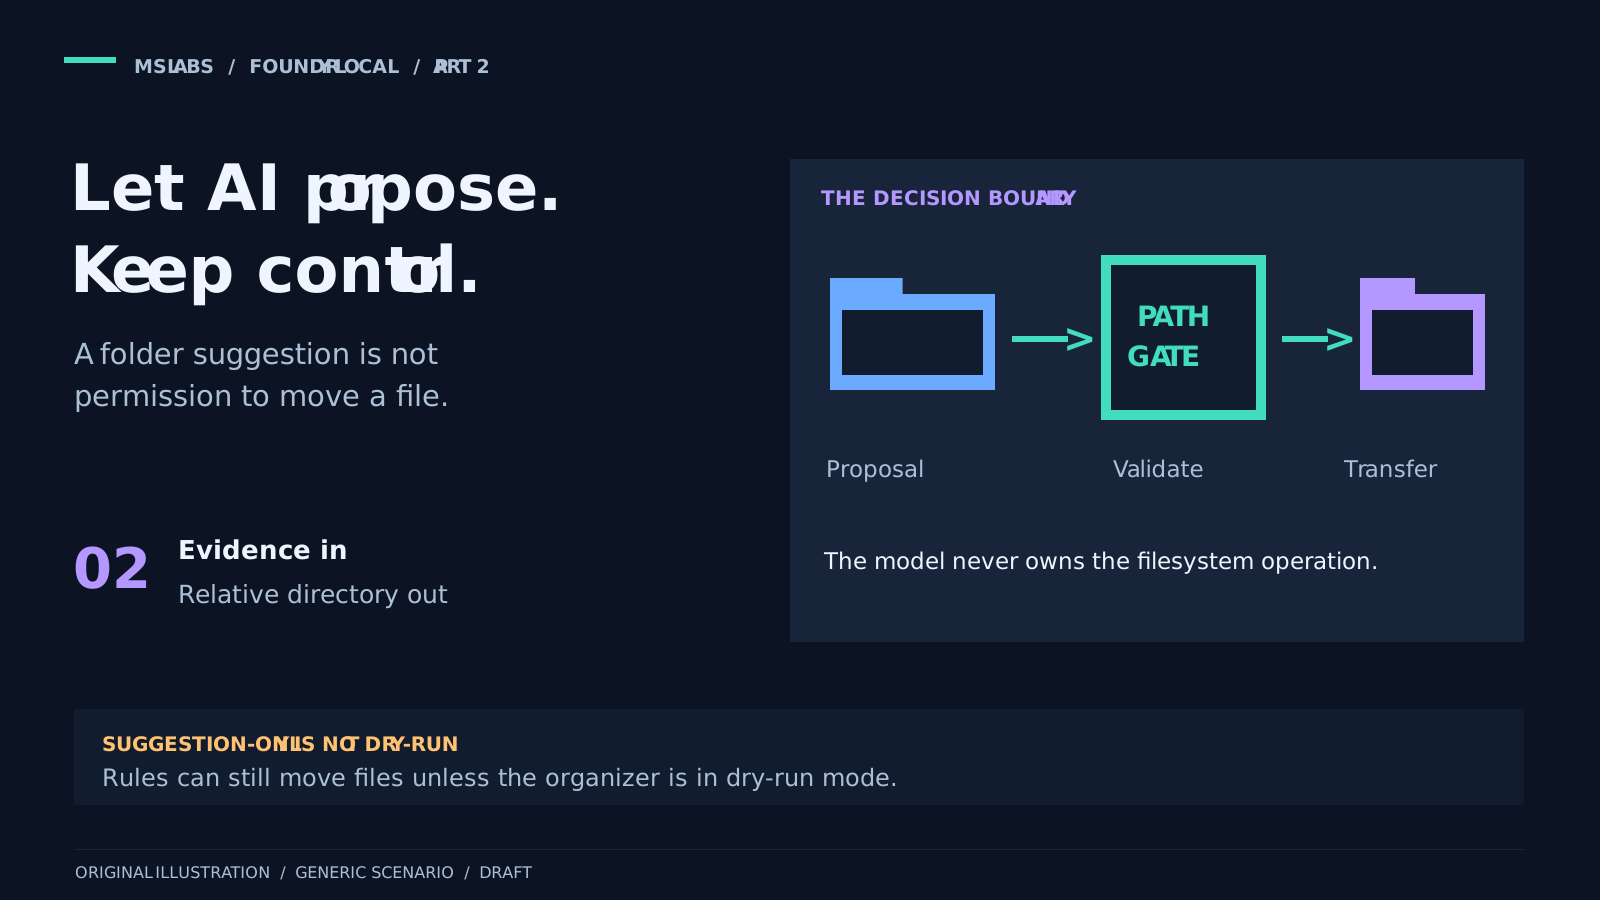
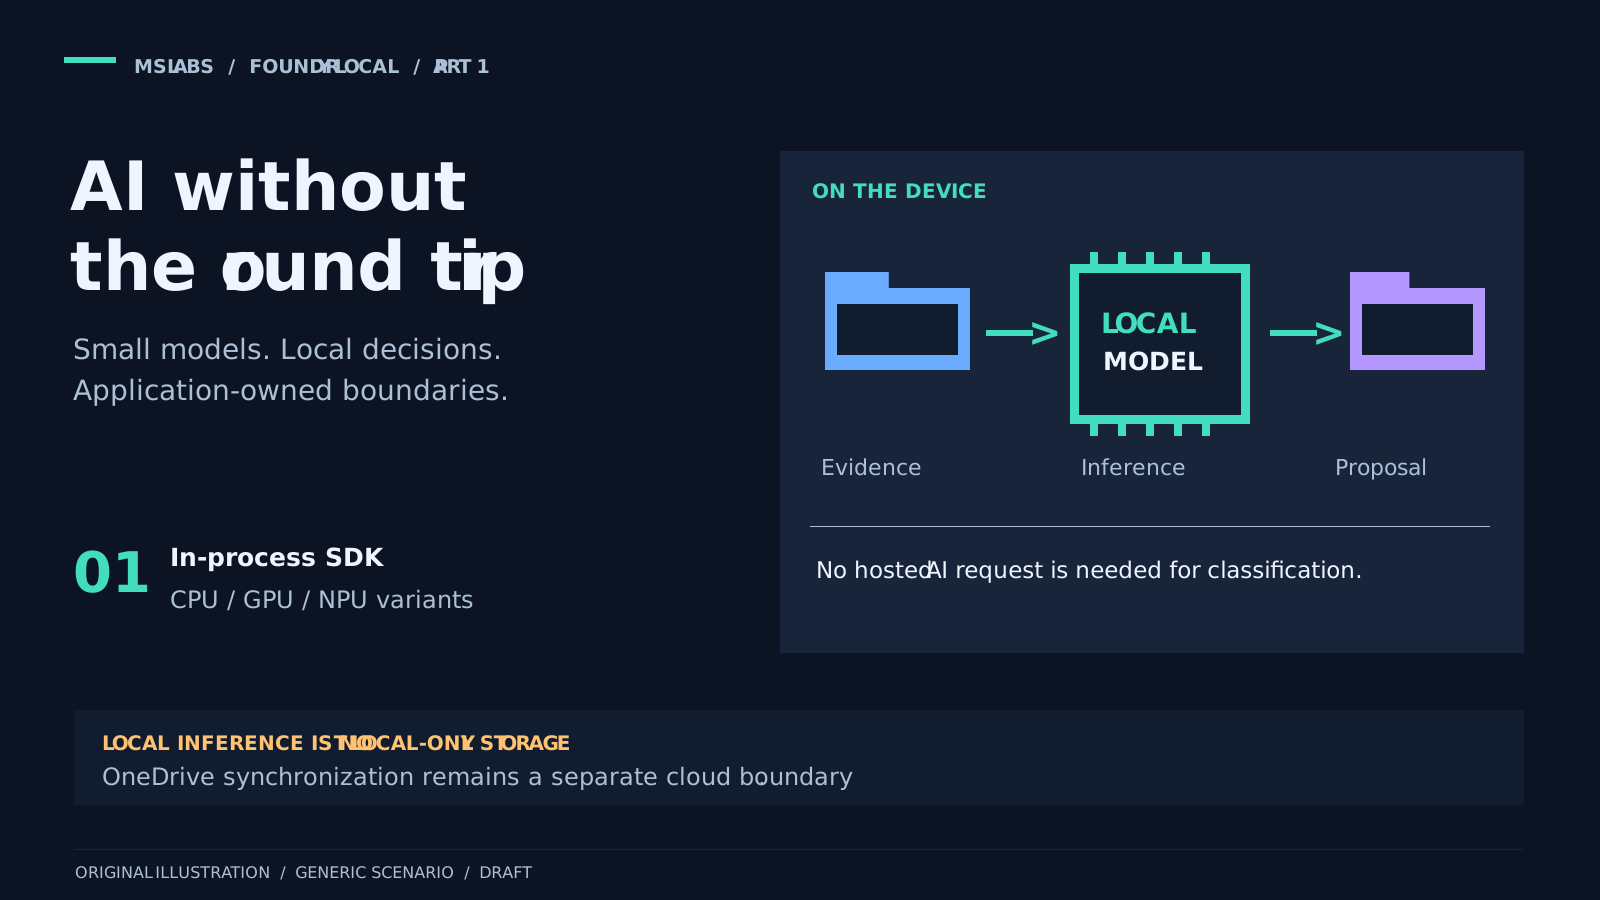
When a filename tells us little, an opt-in local excerpt can help suggest a folder. Here is the code that checks the document, the answer and the allowed categories.
Foundry Local: from local inference to useful file organization · Part 1
Foundry Local · Local AI · ONNX Runtime · OneDrive · .NET
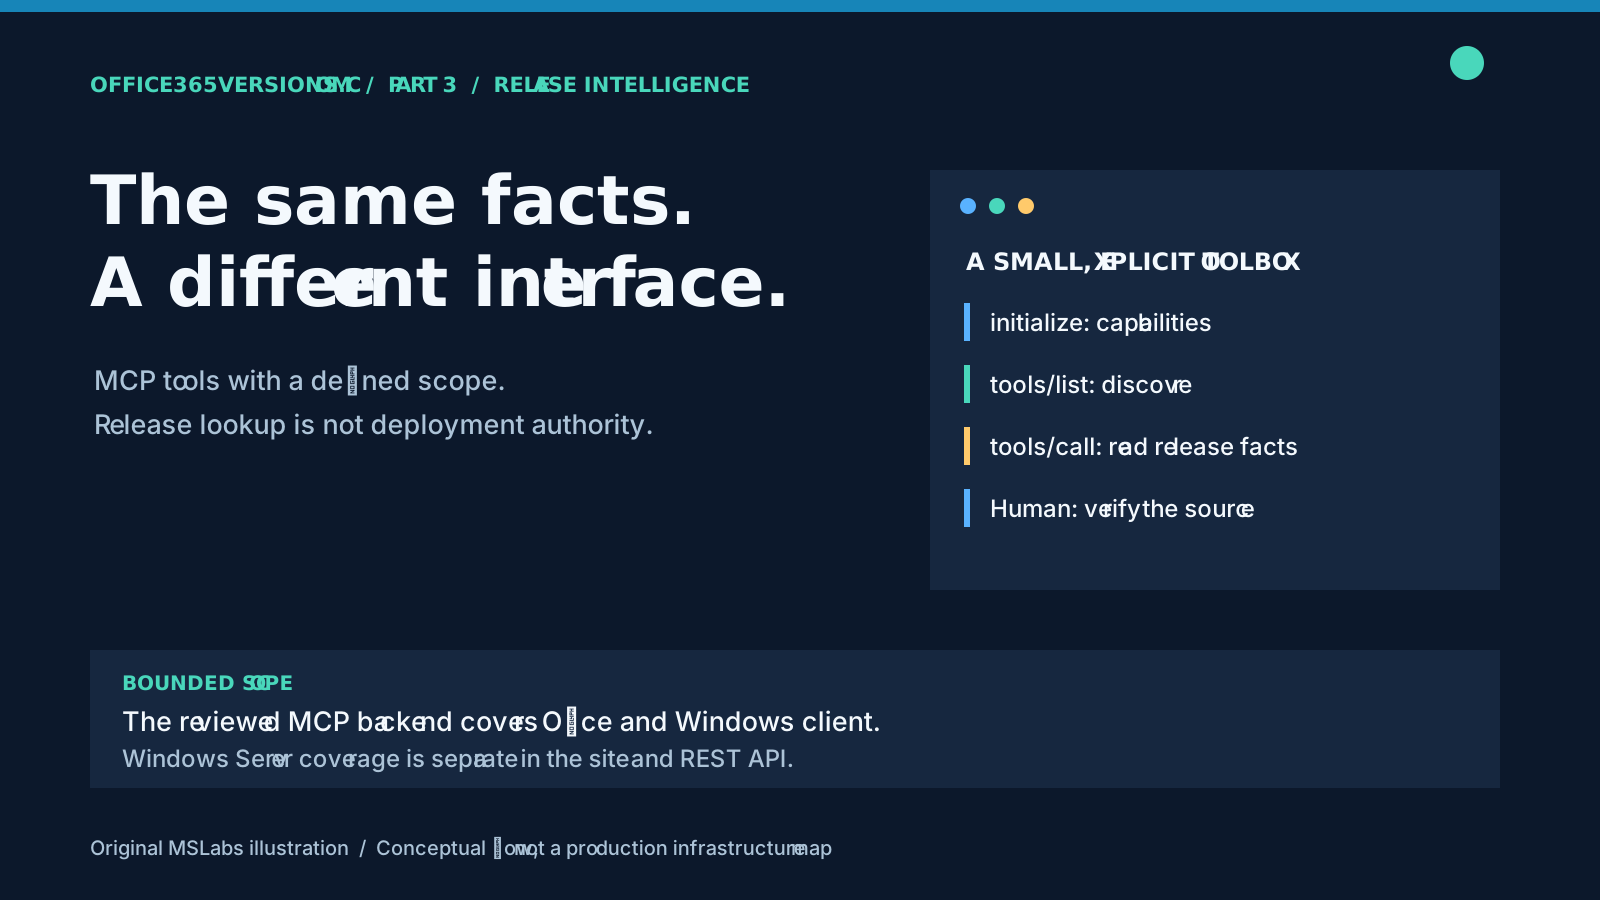
Choose REST endpoints for Office and Windows release lookups, preserve download and servicing context, and handle gateway errors and stale cached data.
Office365Versions.com: release facts for people, scripts and assistants · Part 1
Microsoft 365 Apps · Windows · Windows Server · Web scraping · .NET
How Office365Versions.com collects release histories, Office download estimates, SafeOS packages and Hotpatch updates, with checks before replacing stored data.
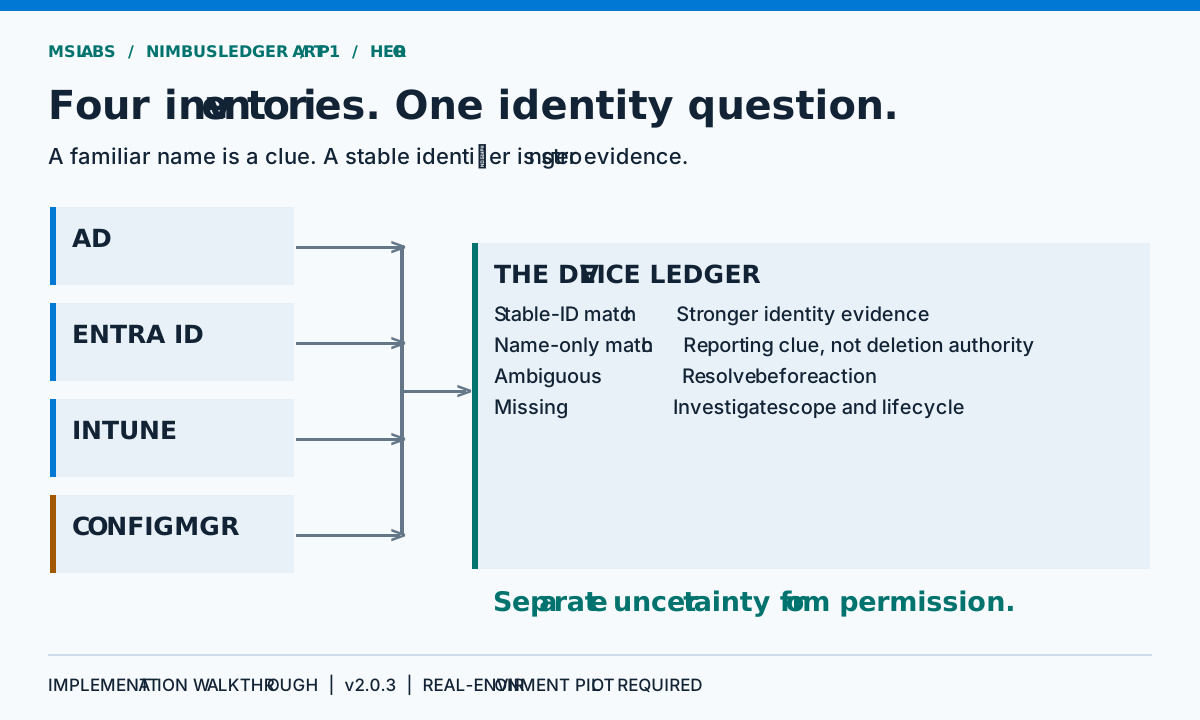
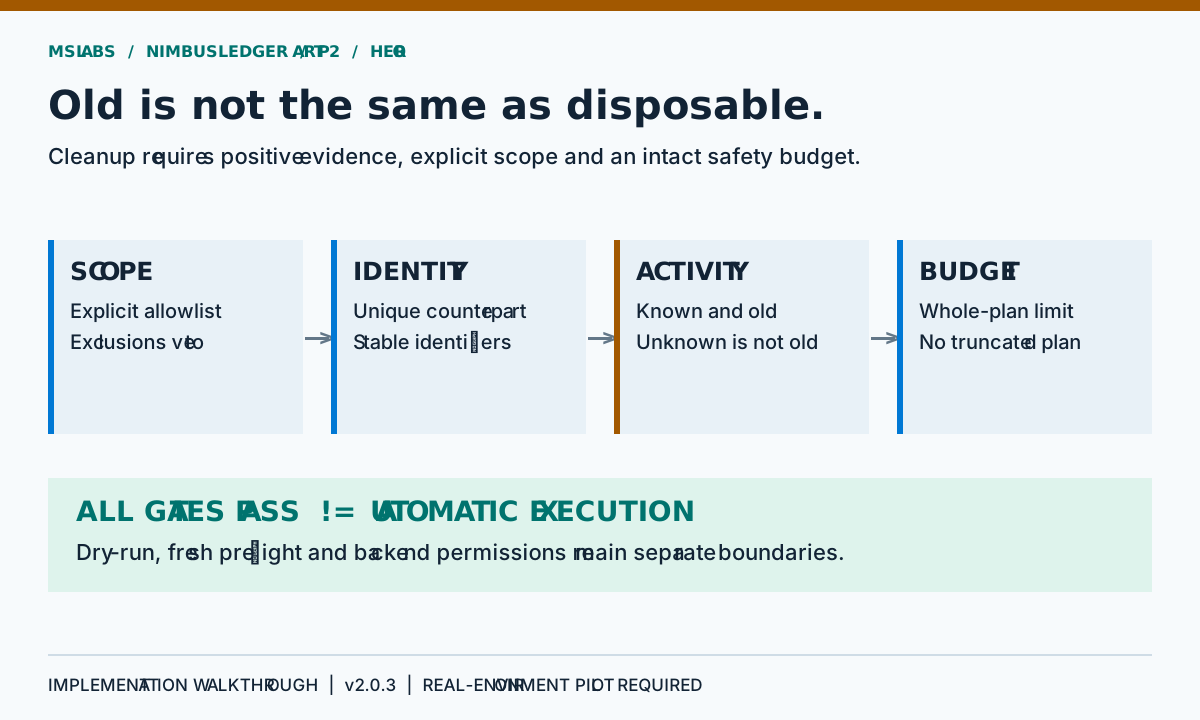
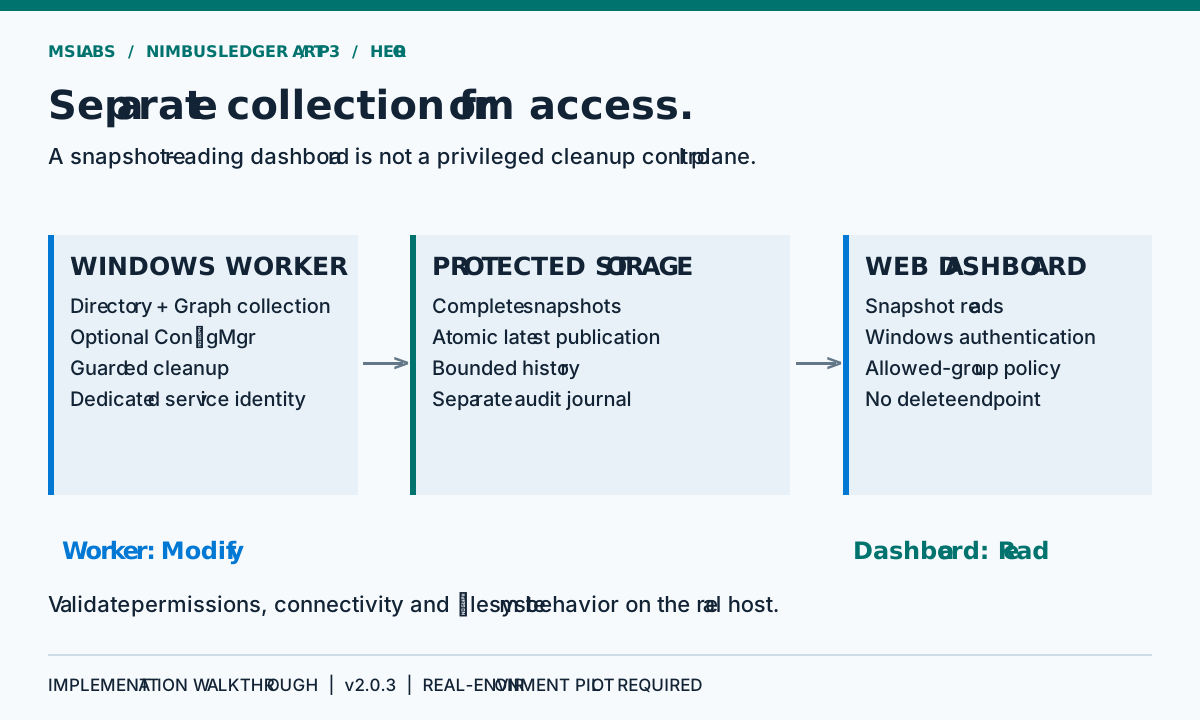
NimbusLedger: from inventory evidence to controlled operations · Part 1
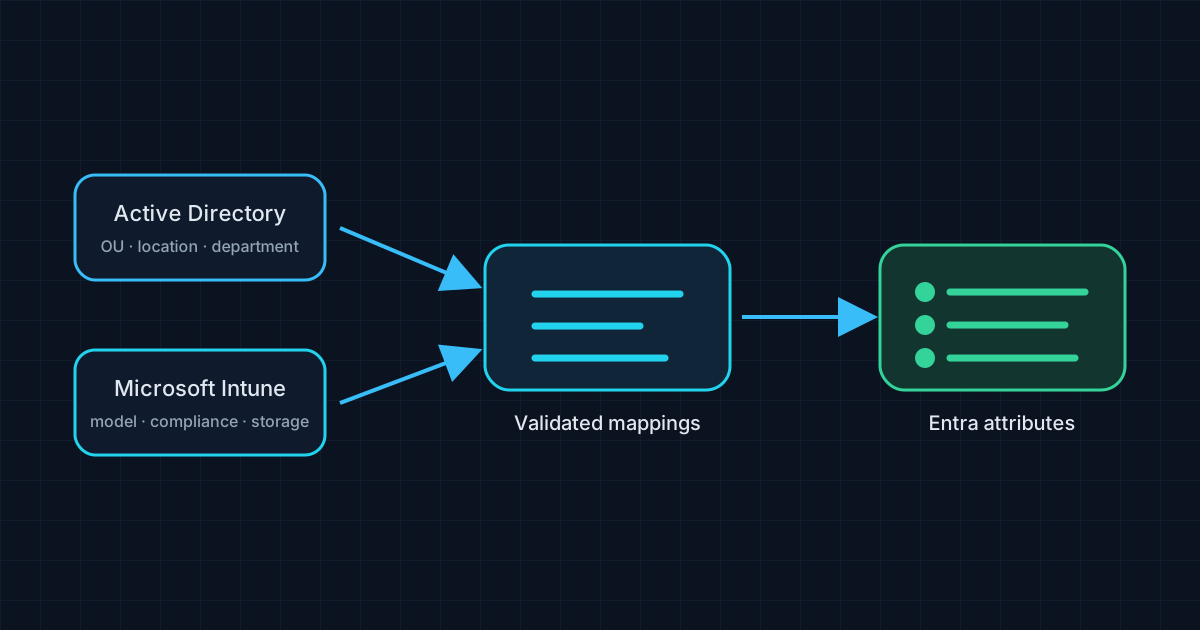
Active Directory · Microsoft Entra ID · Microsoft Intune · Configuration Manager · Device inventory
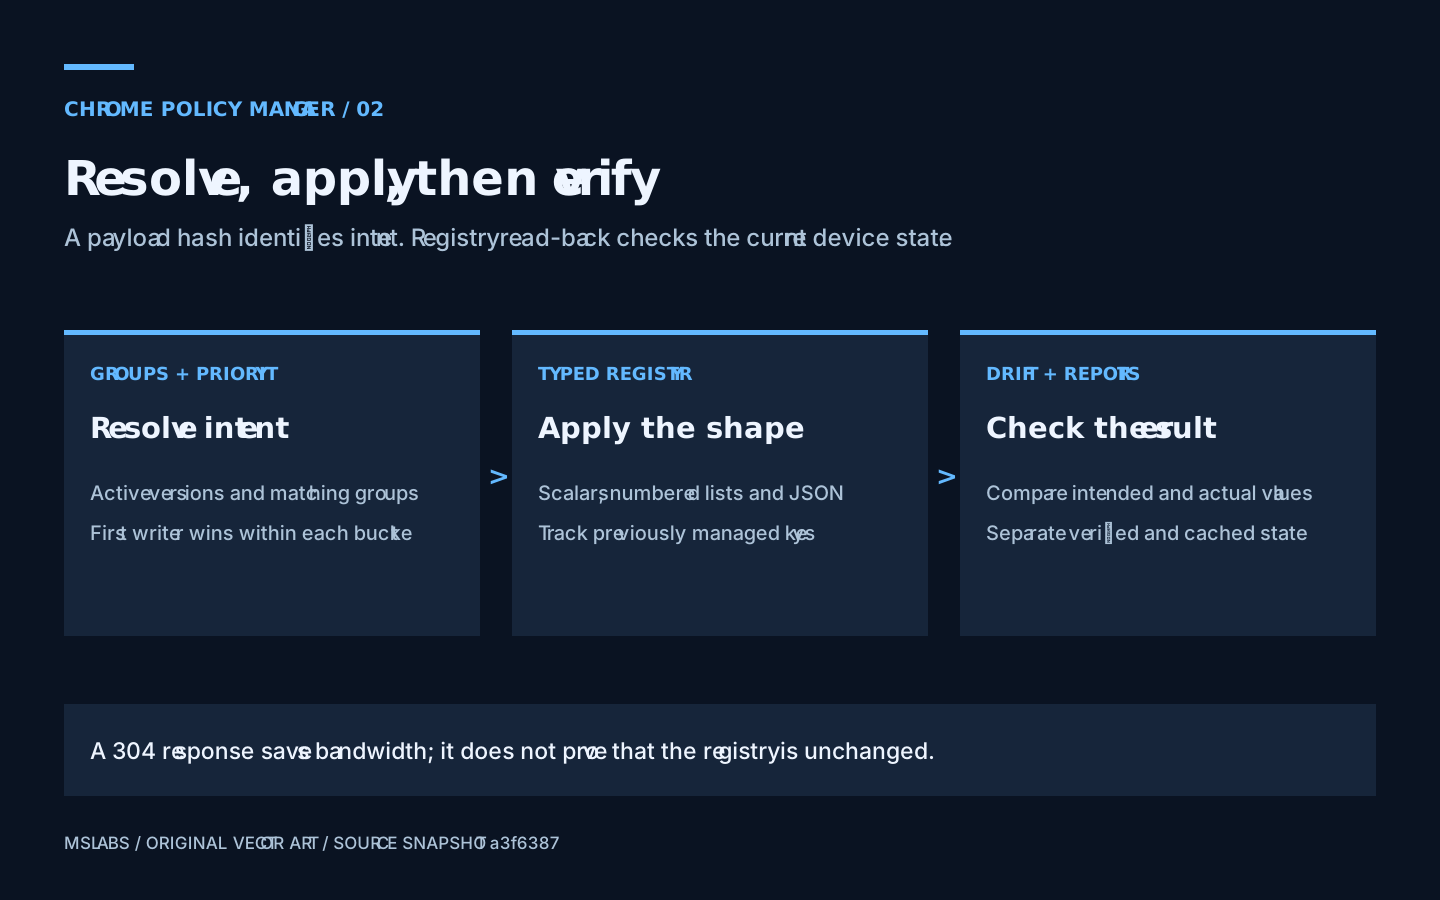
Follow settings from group lookup to registry read-back, and see why an unchanged server hash or cached success can still leave a device needing attention.
Chrome Policy Manager: from intent to verified policy · Part 3
Microsoft Intune · Chrome Enterprise · PowerShell · Entra ID · Azure
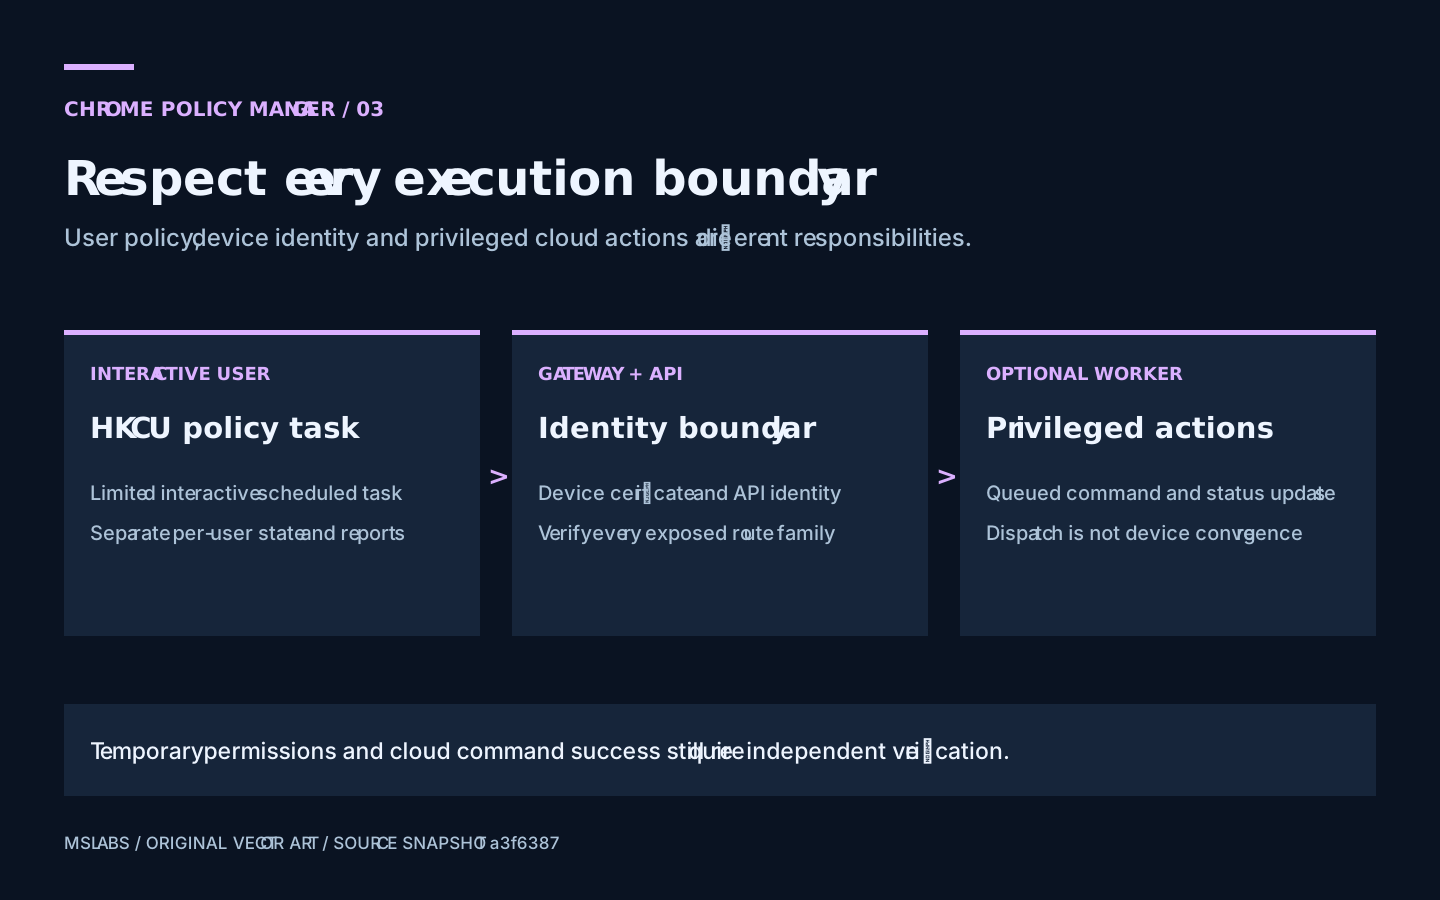
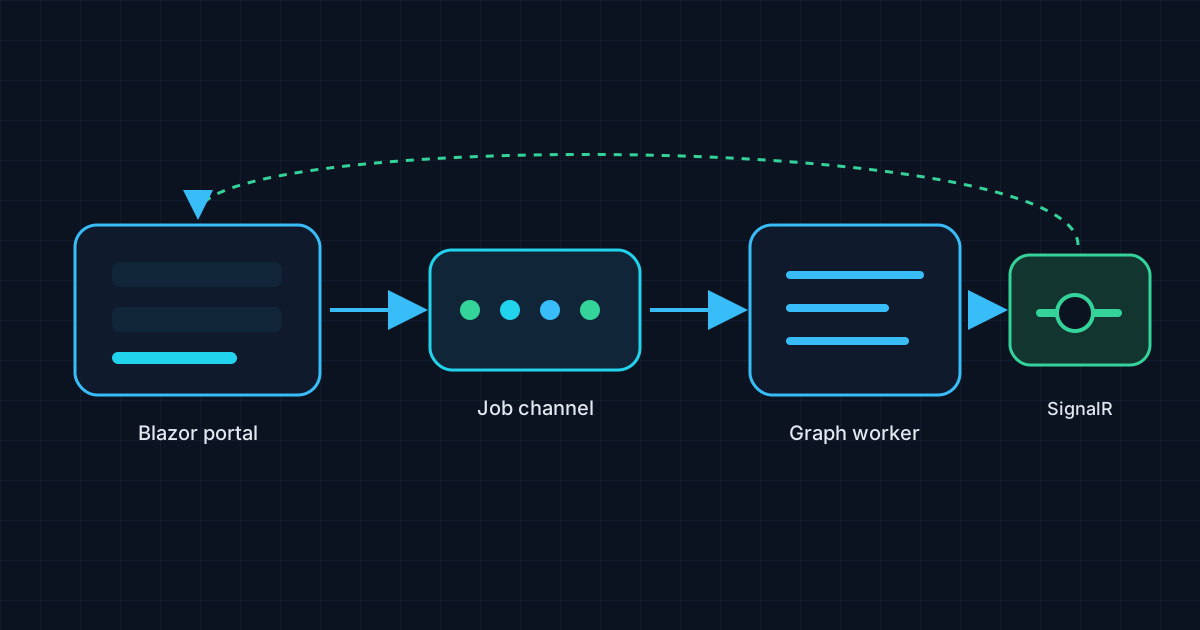
Check user-session tasks, temporary permissions and API identity controls, then follow queued Graph actions without mistaking a dispatch result for applied browser policy.
BitLocker startup PIN without ServiceUI · Part 1
Microsoft Intune · BitLocker · PowerShell · Windows security · Native APIs
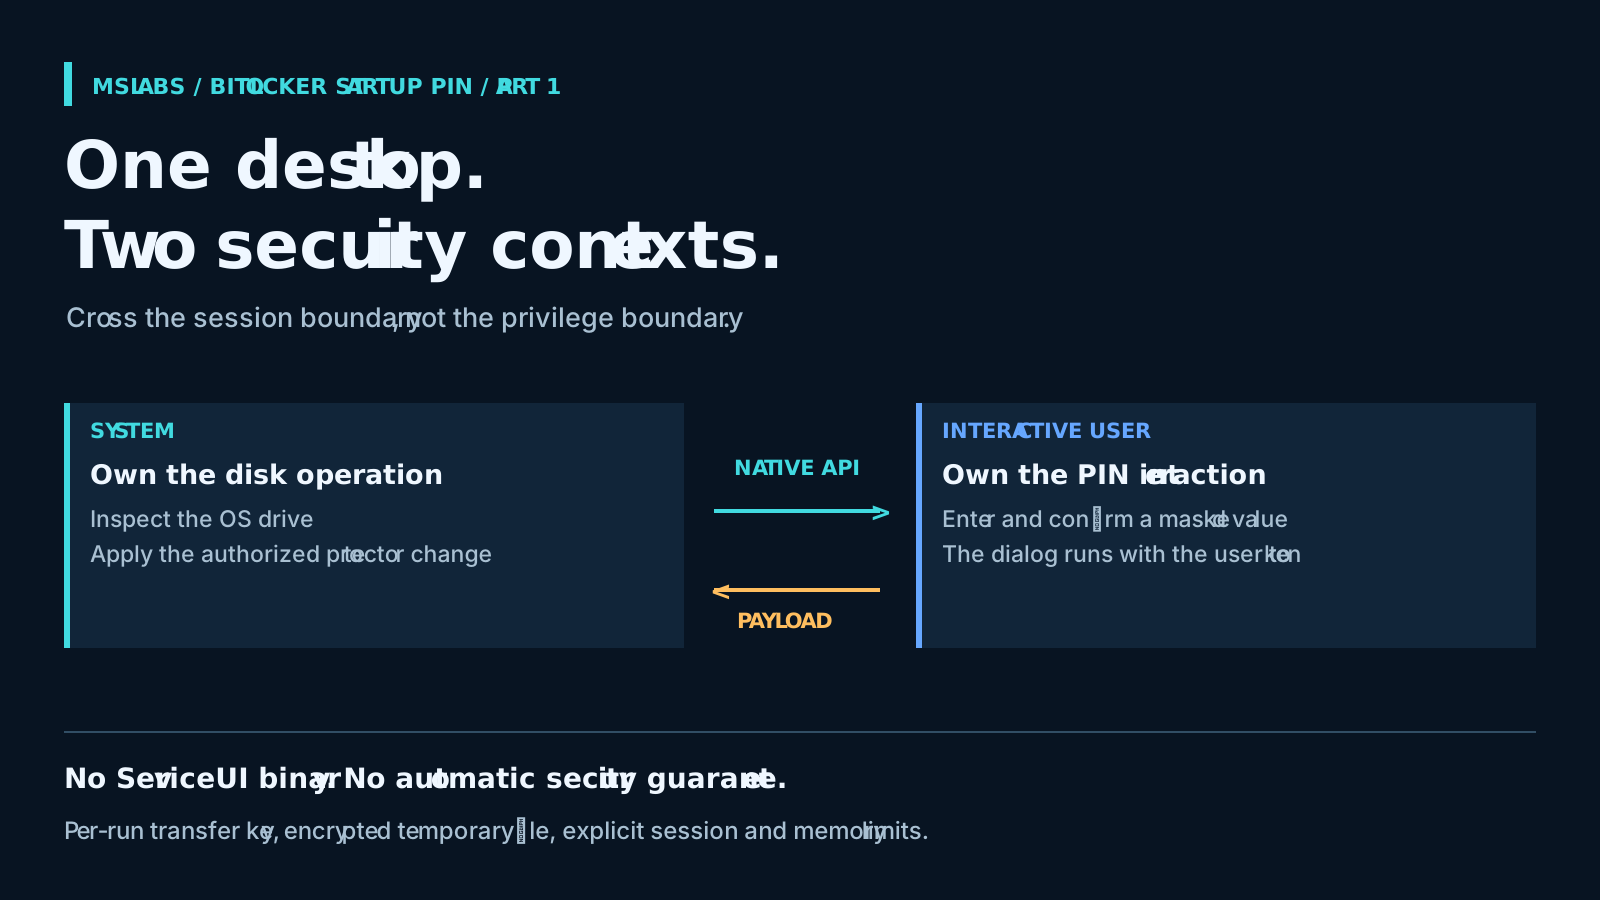
See how SYSTEM launches a user-session PIN dialog and receives an encrypted response, then check the session, memory, timeout and recovery assumptions before rollout.
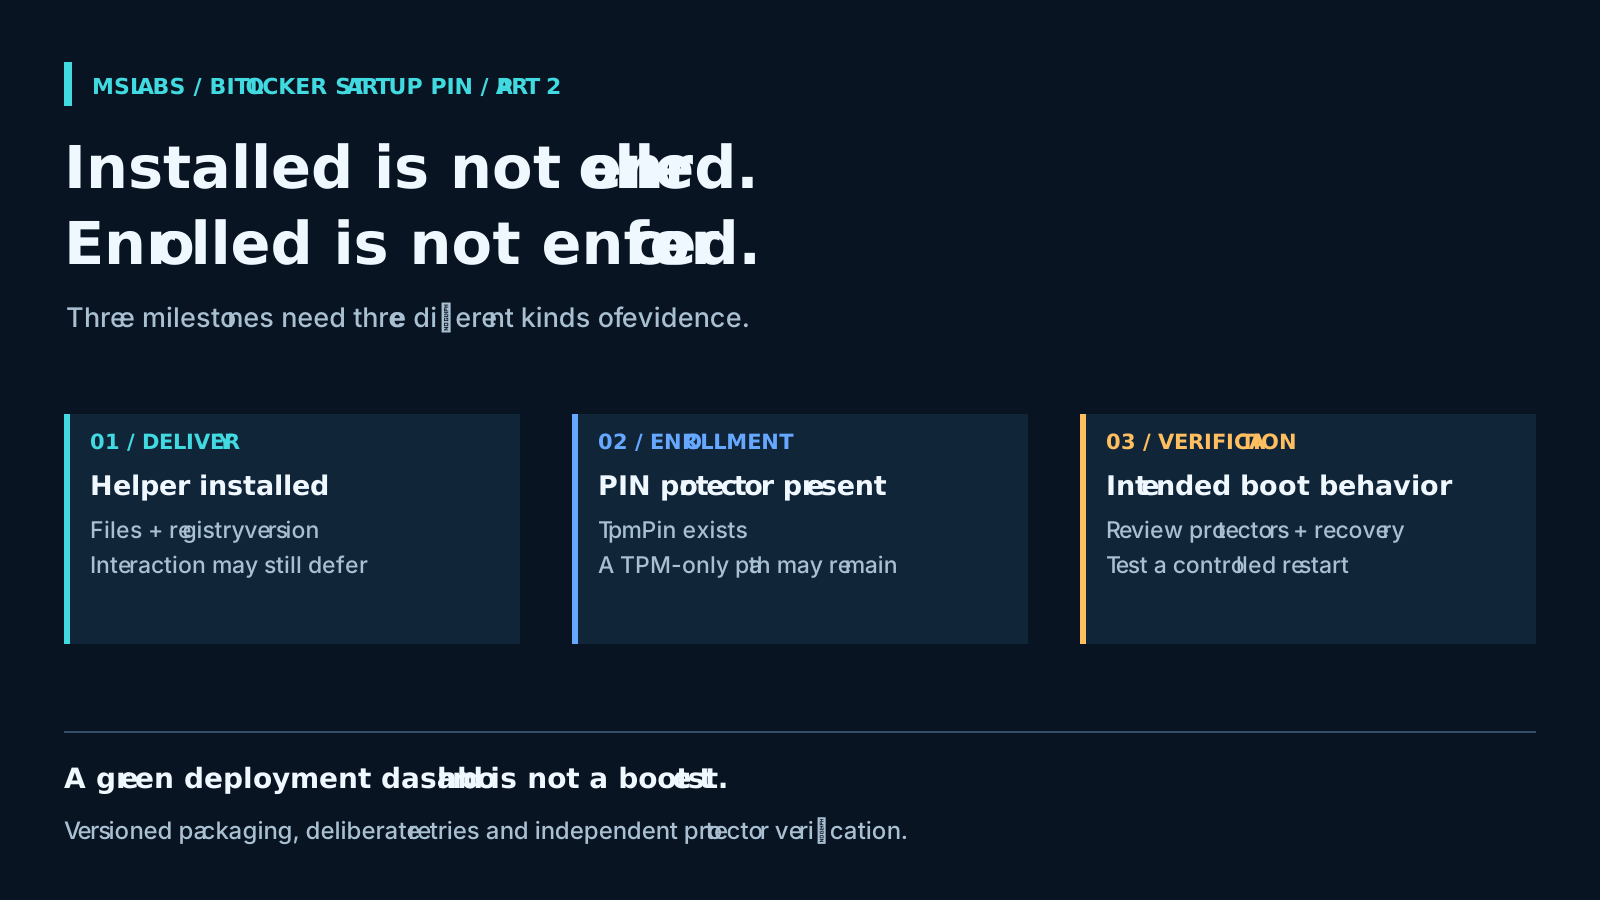
Deploy the helper through Intune, choose a retry route, and verify the laptop's actual boot behavior. Installation success and a present PIN protector each tell only part of the story.
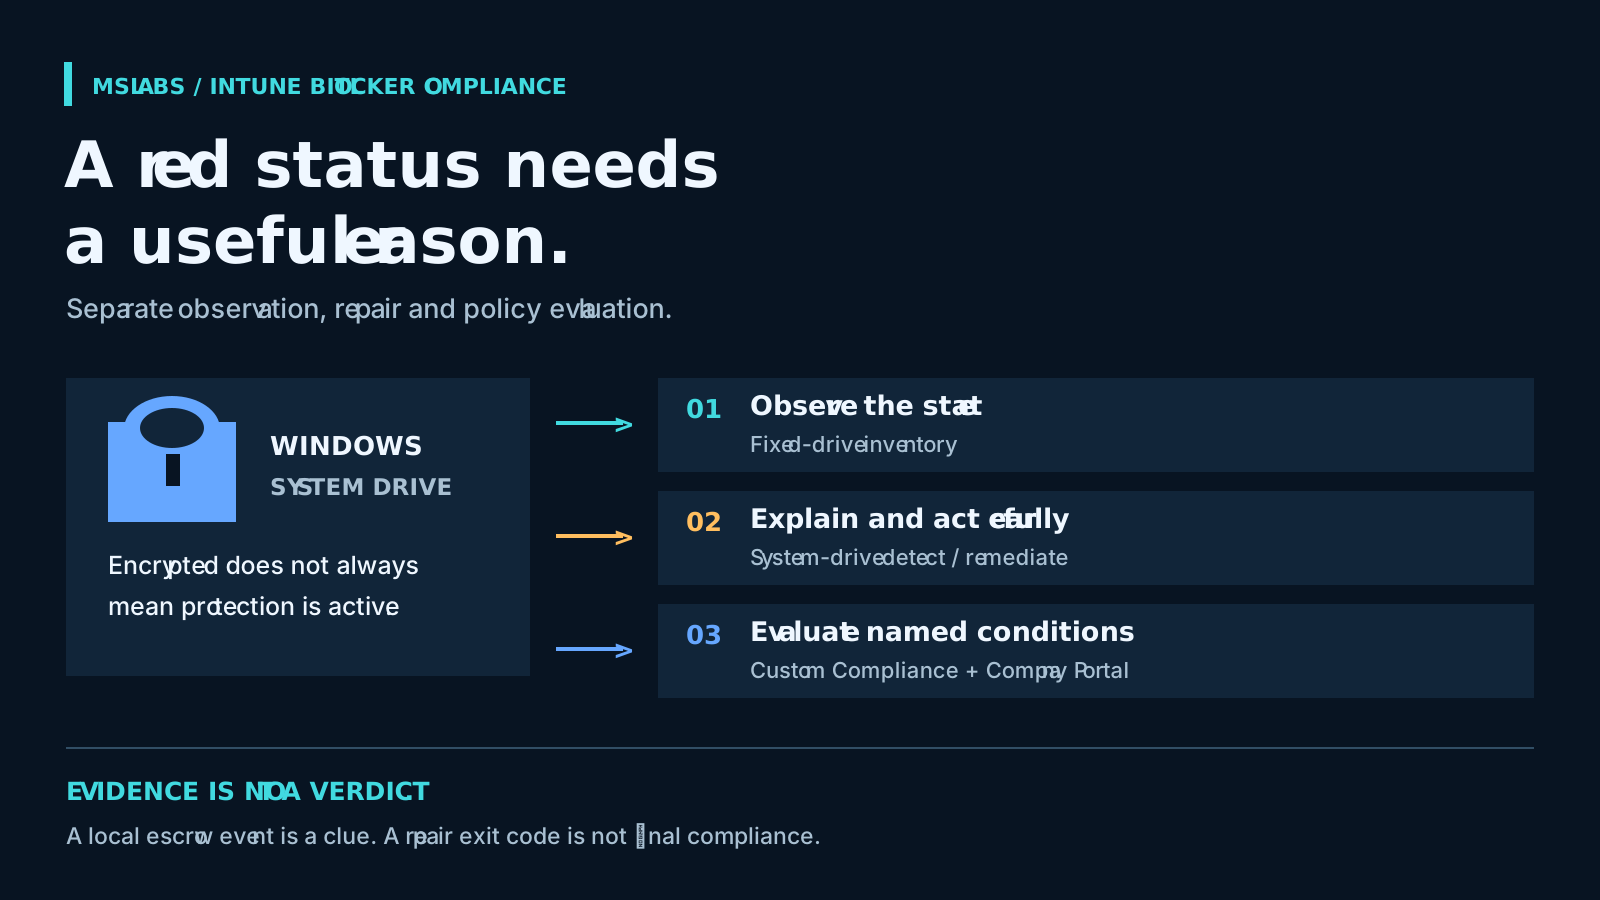
Find out why an encrypted device can fail compliance, what the repair script can fix, and where local escrow clues, policy differences and truncated reports can mislead.
Delivery Optimization · Intune · Azure Functions · Log Analytics · mTLS · Service Bus · Bicep
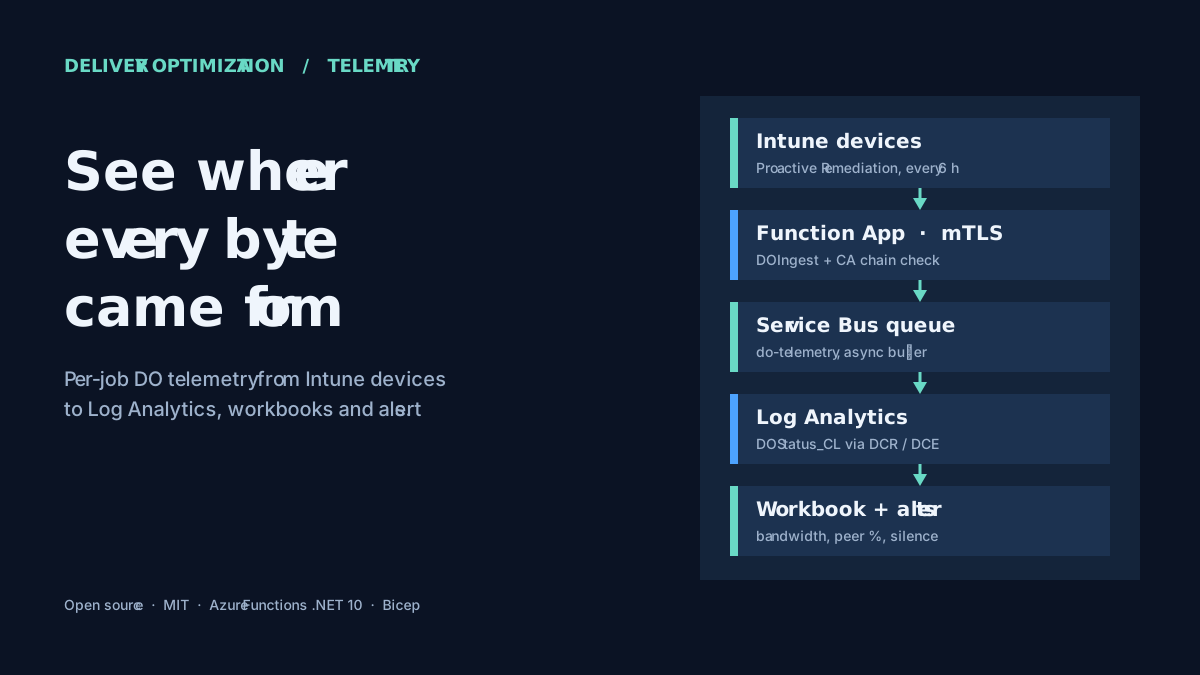
Collect Delivery Optimization job data from Intune-managed devices and use an Azure pipeline, workbook and alerts to see where download bytes come from.
Affinity Studio · SVG · Technical diagrams · Open source · Design systems
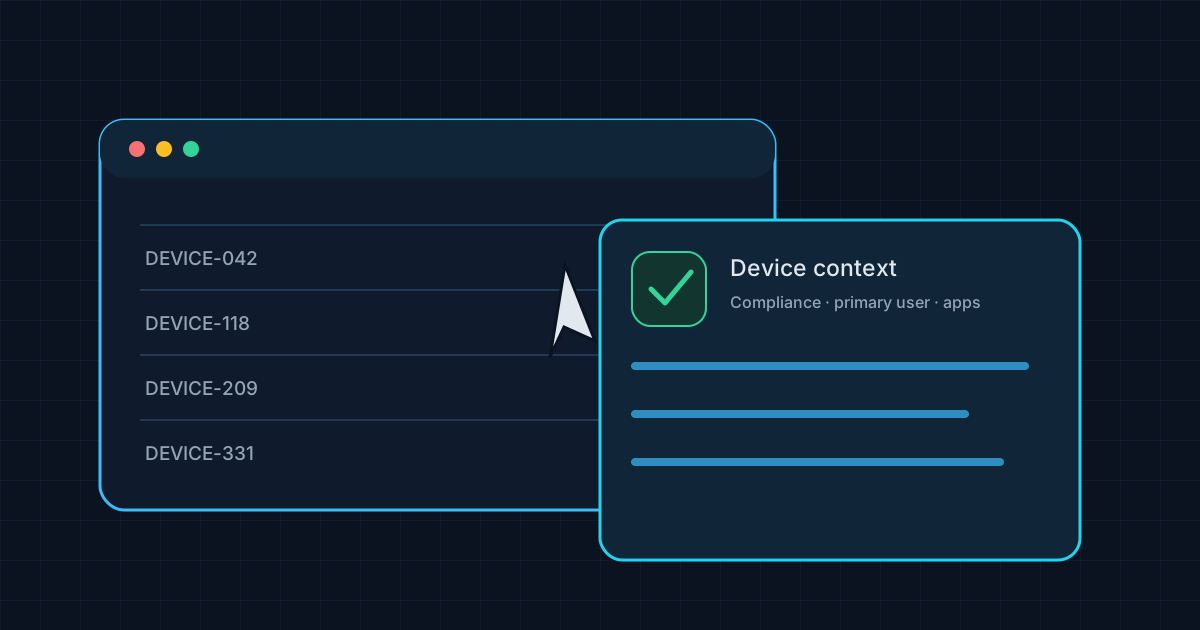
How device lookup, operator access, LAPS sessions and an optional gateway fit together, and what they do not guarantee about reachability or audit records.
Device Operations Bridge: accountable support for cloud-managed Windows devices · Part 3
Windows LAPS · Privileged access · Session management · Microsoft Graph · Secure vault · Security boundaries
Where a LAPS password goes during support, why closing a session does not always rotate it, and how one-time vault links differ from credential-returning tools.
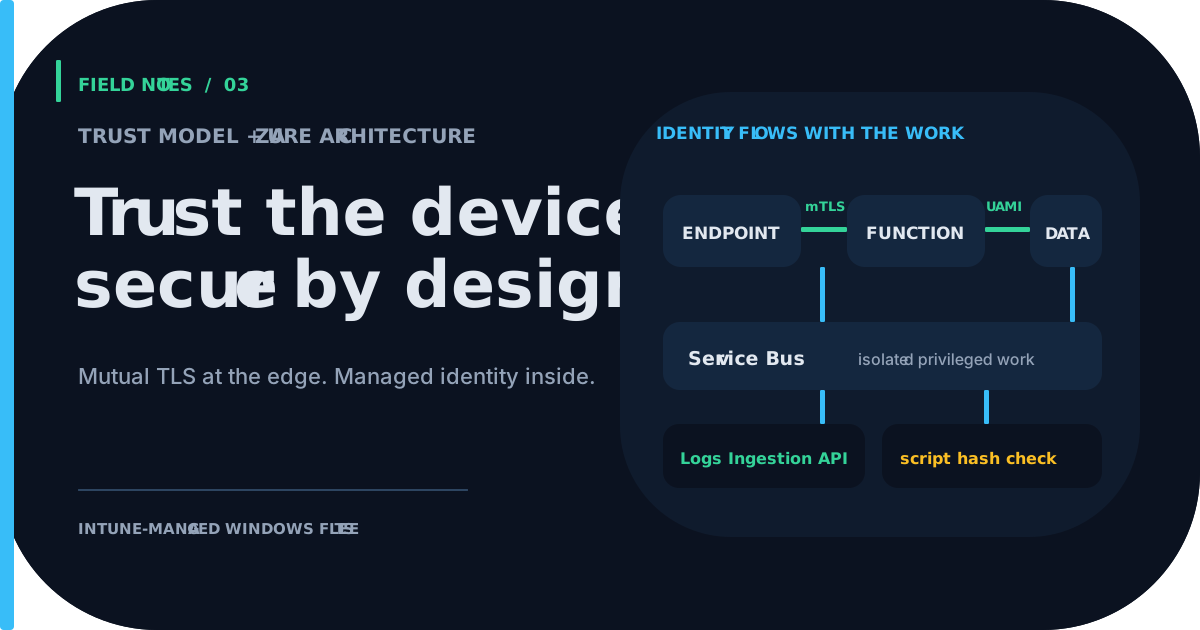
FleetKeeper: operational automation for Intune-managed Windows fleets · Part 3
Azure · Bicep · Service Bus · Managed Identity · mTLS · Security
The Azure services behind FleetKeeper, how device certificates and managed identities are checked, and where script hashes and webhook checks still need other controls.
FleetKeeper: operational automation for Intune-managed Windows fleets · Part 2
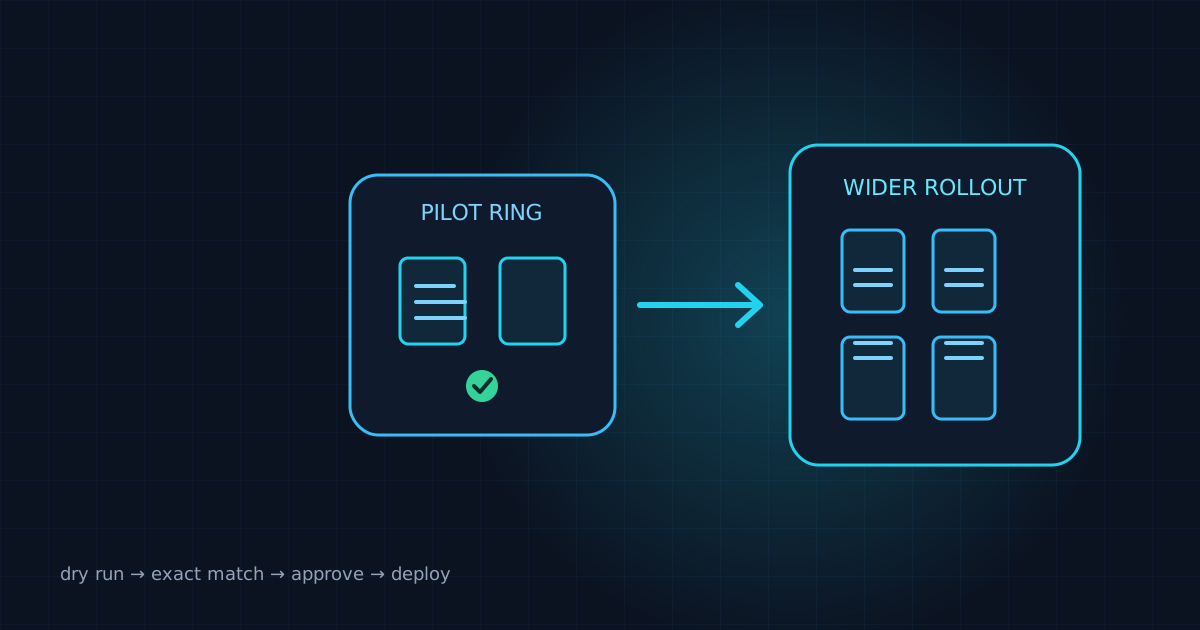
How FleetKeeper stages remediation, rechecks exclusions at plan time and stops a feature after too many reported failures, including the limits of on-demand actions.
FleetKeeper: operational automation for Intune-managed Windows fleets · Part 1
Intune · Remediations · Azure Functions · Windows · Automation
How enterprise PKI and Intune MDM certificates pass separate trust checks, resolve to an Entra device ID and face device-binding and Graph authorization checks.
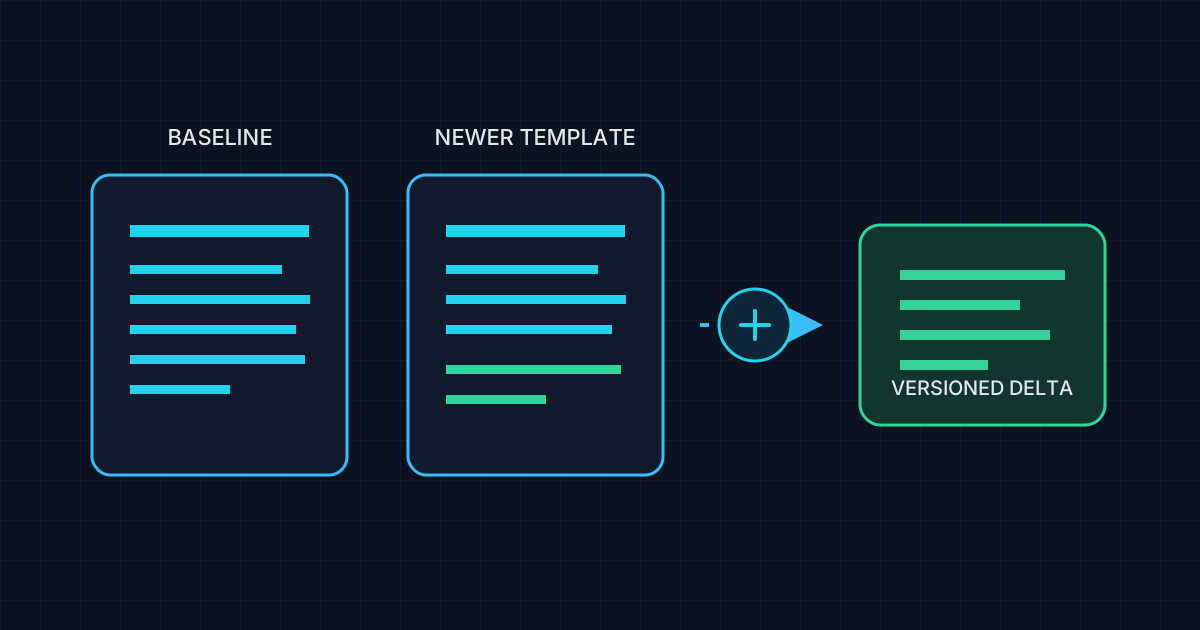
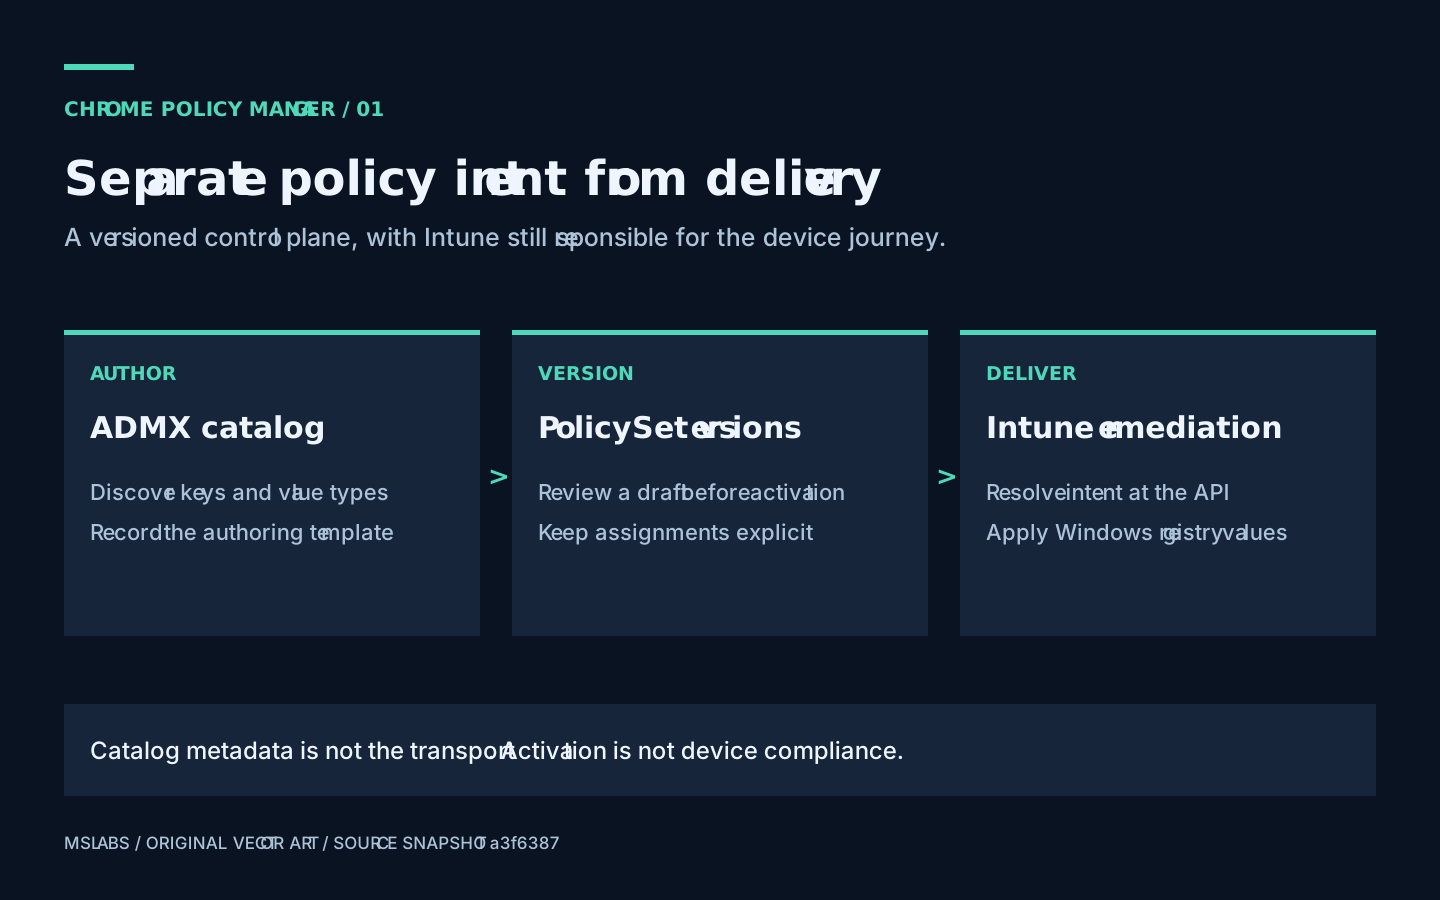
A new Chrome template brings all the old policies too. ADMxSqueezer extracts the additions and their dependencies into a smaller package to test in Intune.
Chrome Policy Manager: from intent to verified policy · Part 1
An overview of certificate-authenticated telemetry, offline delivery and Azure ingestion, with the hosting and packaging constraints worth checking before deployment.
LogCollector: authenticated telemetry for Intune devices · Part 2
How the client keeps unsent telemetry in a bounded spool, retries with fresh signatures and ships through Intune with detection generated from the installed configuration.
LogCollector: authenticated telemetry for Intune devices · Part 1
Why the retired Data Collector API needed more than a new URL, and how device certificates, signed requests, replay checks and managed identity replace shared workspace keys.
BitLocker Key Monitor: proving recovery keys exist · Part 3
Security Architecture · Encryption · SQL Server · BitLocker
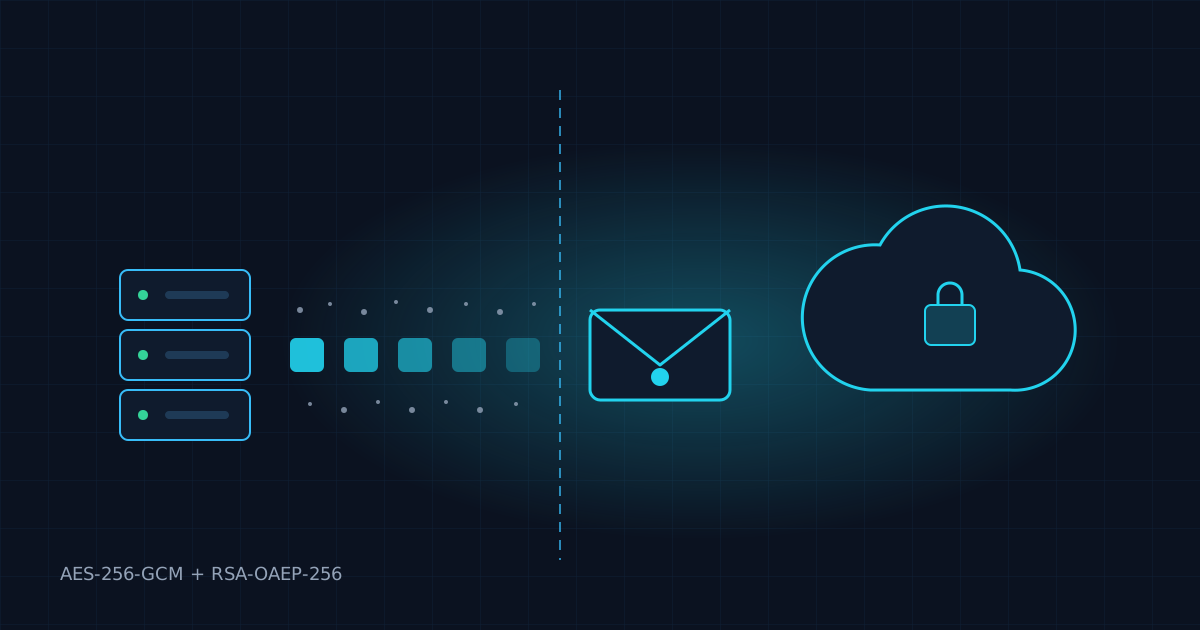
Part 3 of 3. Encrypt recovery values before SQL storage, bind them to their rows, and understand what still depends on key handling, migration and operator controls.
BitLocker Key Monitor: proving recovery keys exist · Part 2
Azure Functions · Key Vault · Security Architecture · Service Bus
Part 2 of 3. Follow an encrypted scan batch from the domain agent to Azure, including size checks, storage verification, retries and the permissions that keep intake out of decryption.
BitLocker Key Monitor: proving recovery keys exist · Part 1
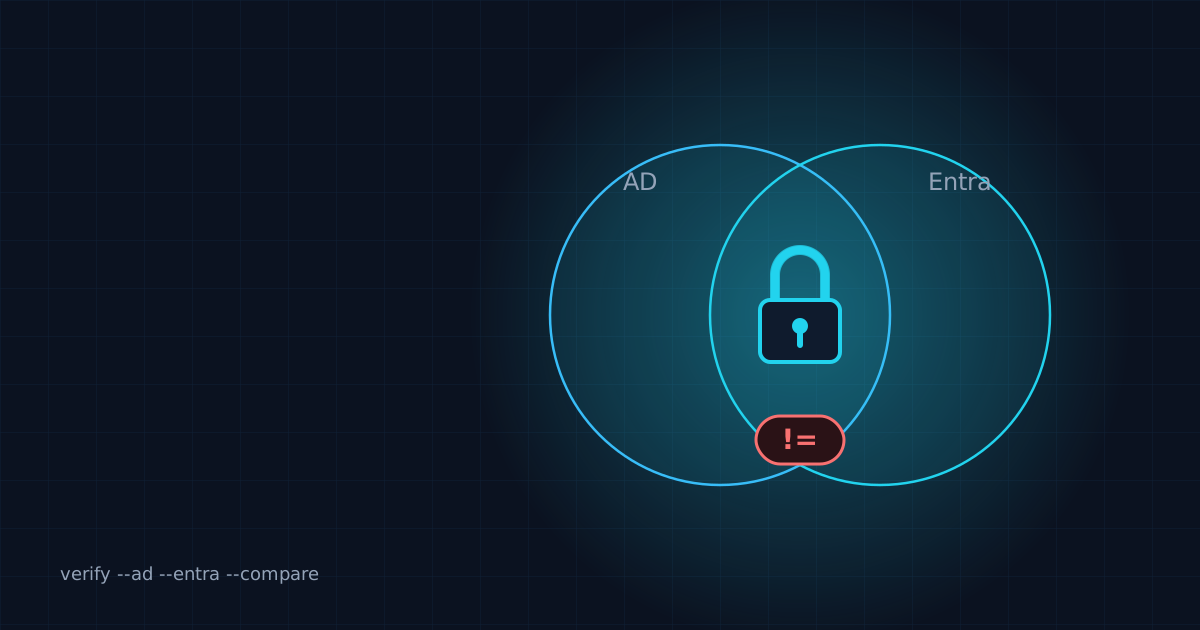
Part 1 of 3. Check where recovery keys are available, resolve device identities carefully, and compare passwords when explicitly enabled rather than relying on presence alone.
Intune · Windows Autopilot · PowerShell · Microsoft Graph · Automation Safety